Category Archives: History

Low Prices Were a Nazi Tool: Isabella Weber’s Anti-Fascist Economics Gets 1936 Backwards

English | Deutsch

Isabella Weber has a new book out. The Guardian profiled it on 16 October: Anti-Fascist Economics: In Defence of Affordability, Dignity and Democracy (Allen Lane). The prescription fits in one sentence, and the article gives it in one: make life’s necessities affordable.

“Fascism is rising from frustration, born out of a crisis of livelihoods,” says Weber. “So, we need to reclaim these essentials now.”

The German record says the opposite. Low prices were a tool of the fascist regime. They did nothing to stop it.

Prices fell every year from 1929 to 1932. Heinrich Brüning governed by emergency decree, cut wages, salaries and benefits and raised taxes; the Bundeszentrale für politische Bildung calls it radical deflation and records the name it earned him, “Hungerkanzler”. His fourth emergency decree of 8 December 1931 went beyond letting prices fall. It ordered them down. Bound prices, meaning cartel and branded-goods prices, had to be cut by at least ten percent against their mid-1931 level from January 1932, under a Reich commissioner for price supervision with powers to enforce it, as a 1933 account from inside the commissioner’s office sets out. Registered unemployment passed six million the same winter.

The Nazi vote rose through every one of those years.

Reichstag election NSDAP share
20 May 1928 2.6 %
14 September 1930 18.3 %
31 July 1932 37.3 %
6 November 1932 33.1 %

Source: Deutscher Bundestag. Seven months after a decree cutting prices by ten percent, the NSDAP took 37.3 percent and became the largest party in the Reichstag.

Weber’s school has an answer to this, and it has evidence. Galofré-Vilà, Meissner, McKee and Stuckler, “Austerity and the Rise of the Nazi Party”, Journal of Economic History (2021), matched voting data from a thousand districts and a hundred cities across four elections between 1930 and 1933 against spending cuts and tax increases, and found higher Nazi vote shares where the cuts went deepest. I accept the finding. Read what it measures. The variable is the state withdrawing: benefits cut, taxes raised. Prices sit outside it, because the same government was pushing prices down at the same time. Austerity and cheap goods arrived together, and the vote went to the party promising work and revenge. Cheap bread bought the republic nothing.

Then the end, which was a transaction. The NSDAP lost two million votes in November 1932. Hindenburg appointed Hitler chancellor on 30 January 1933 after that loss, in a cabinet arranged by Franz von Papen and the conservatives around the president. The Reichstag Fire Decree of 28 February suspended civil liberties. The election of 5 March was held under SA terror. The Reichstag passed the Enabling Act on 23 March, and the law of 14 July 1933 made the NSDAP the only legal party. Appointed, then entrenched. A majority voted for it at no point.

The regime then did what Weber recommends. On 26 November 1936 the Reich commissioner for price formation issued the Verordnung über das Verbot von Preiserhöhungen, a general ban on price increases for goods, services and rents, pegged to the level of 18 October 1936; the Berlin Institut für Konjunkturforschung reported the decree the week it came out. In March 1937 the same institute recorded that wholesale and retail prices still stood a fifth to a quarter below their 1928/29 peak. The freeze capped the inflation that rearmament on MEFO bills had built up. Adam Tooze sets out the mechanism in The Wages of Destruction (2006): prices held on paper while quality fell and goods ran short, the fat shortage of 1935 and 1936 being the case the regime could least hide. The regime delivered the appearance of affordable essentials, and the appearance was enough.

Götz Aly went further in Hitlers Volksstaat (2005): the regime bought loyalty with tax relief and benefits financed by plunder and “Aryanisation”. The thesis is contested. Tooze answered in the taz that Aly had grossly underestimated what the war cost Germans by counting taxes and leaving out the bonds; Johannes Bähr called the book the legend of the “Wohlfühldiktatur”. That dispute is about who paid. On the point that matters here the parties agree: cheap essentials, real or staged, were a technique of the regime.

A democracy whose case rests on cheap essentials has no answer when a strongman delivers them cheaper, and that’s what 1936 shows.
Weber’s own example in the article shows the mechanism running today. Mexican retailers cap the total price of a basket of two dozen essentials, the canasta básica, and the government rewards them with tariff and tax relief, “and at a weekly press conference lauds those who do a good job and calls out those who don’t”. The article’s verdict: “In Mexico’s 2024 presidential election, the governing Morena party increased its vote share from 55% to 61%.”

The same governing party then spent the mandate. In September 2024 Congress passed, and a majority of states ratified, the judicial overhaul that puts every judge in the country up for popular election. Eight of the eleven justices of the Supreme Court, the chief justice among them, resigned rather than stand. Affordability bought votes for a government concentrating power. The example argues against the book that cites it.

The demagogue can promise without delivering and blame an enemy when the promise fails. Donald Trump in Bozeman, Montana, 9 August 2024:

Starting on day one, we will end inflation and make America affordable again, to bring down the prices of all goods.

Trump at a cabinet meeting, 2 December 2025:

Look, affordability’s a hoax that was started by Democrats who caused the problem of pricing.

That is the full cycle in sixteen months. An economist who builds democracy’s case on affordability competes on the demagogue’s terms, and the demagogue is free to lie.

The article closes with family.

Family legend is that her grandfather, a priest in the Ruhr Valley, refused to hang a swastika in his church.

The sentence is the journalist’s, and “family legend” is his phrase. The grandfather goes unnamed. The legend is the whole evidence.

The records exist, and they are open. A priest with grandchildren in the Ruhr is in all likelihood an evangelischer Pfarrer. The Protestant church kept personnel files on its clergy, and those files sit in the Landeskirchliches Archiv of the Evangelische Kirche von Westfalen in Bielefeld or the Archiv der Evangelischen Kirche im Rheinland in Düsseldorf, depending on the parish. The NSDAP membership card index sits in the Bundesarchiv, which states on its own site that a signed application was a condition of admission. The denazification files for all of North Rhine-Westphalia sit in the Landesarchiv NRW in Duisburg, which put about 610,000 of them online in August 2023, searchable by name.

The swastika in the church is itself a documented question. Decorating churches with swastikas was the practice of the Deutsche Christen, the Nazi faction that won the church elections of July 1933. Pastors who refused left records: Otto Mörike in Württemberg demanded in March 1933 that the flag come down from his church tower, and his Landeskirche’s own flag decrees of that spring are in the file. So the question a record answers is which side the grandfather’s church stood on, Deutsche Christen or Bekennende Kirche. A legend answers nothing. I make no claim about who he was or what he did. The point is that she offers legend where records exist.

Her grandfather story is the national pattern, not an exception. Harald Welzer, Sabine Moller and Karoline Tschuggnall interviewed forty German families for “Opa war kein Nazi”. Nationalsozialismus und Holocaust im Familiengedächtnis (Fischer, 2002). Families keep the official story of German guilt and move their own grandparents across to the bystanders, the victims and the resisters, and with each generation the grandfather improves. The authors’ term is kumulative Heroisierung.

The other side of German politics tells the same story. Friedrich Merz on his grandfather Josef Paul Sauvigny, mayor of Brilon from 1917 to 1937:

Date Statement or record
2004, Merz in writing Grandfather entered the NSDAP “ohne eigenes Zutun”, had “geweigert” to join, was “kein Nationalsozialist”
January 2025, Merz in the Zeit podcast “Alles gesagt” Grandfather “in diese Abgründe des Nationalsozialismus hineingeraten”
March 1936, Landrat’s file note Sauvigny “von Anfang an als SA-Mann eifrig betätigt”
Personnel file, Landesarchiv NRW Membership application made between May 1933 and February 1936
NSDAP card index, Bundesarchiv Member from 1 May 1937

Kersten Augustin and Martin Teigeler published the files in the taz on 8 May 2025. Merz did not answer the taz. One detail from their piece: the 2004 wording from Merz matches almost word for word the statement his grandfather gave the denazification committee in 1946 to clear himself. The family legend was the grandfather’s own Persilschein, handed down intact.

A conservative chancellor and an anti-fascist economist tell the same family story. The pattern is national, not partisan.

Dignity is in the title of the book. In the record, the regime that froze prices also stripped dignity from everyone it chose, and the freeze helped it hold the rest. A democracy whose case rests on cheap essentials has no answer when a strongman delivers them cheaper, and that’s what 1936 shows.

The Only Breached Company to Call Its Attacker Unsophisticated Was Suing Someone Else

Just once, I’d like to see a company come forward and say “we got badly breached, and we analyzed the evidence, and you know what, we don’t think the adversary was extremely sophisticated at all”

Michal Zalewski (lcamtuf) asked for that sentence in Fediverse. I replied “challenge accepted”, as a matter of historical record.

In twenty years of breach disclosures I have found it exactly once, in 2025, in a lawsuit that put the blame on a vendor anyway. Regulators are the ones who write it often, usually a year or two after a chief executive put the word “sophisticated” into a press release. The herd of chief executives (ironic, no?) reaches for “sophisticated” by reflex. Only a thin file of them said something closer to “oops, duh” than “wow, who could have known.”

This post is a trip down memory lane, and it collects exact quotes, with links to the filing, transcript, penalty notice or original report where it appears. It’s similar to posts I’ve done in the past, but more targeted to the question of accepting fault.

1755

Let’s talk about “sophisticated” as a particular term in breach disclosure defense filings. I have called it out since at least 2011 when I gave a series of talks about state-level breaches, attempting to convince our industry to stop using the word.

Samuel Johnson defined it in his 1755 Dictionary as “To adulterate; to corrupt with something spurious.” For the noun, he quoted medical writer John Quincy: “the act of counterfeiting or adulterating any thing with what is not so good, for the sake of unlawful gain.” Merriam-Webster still gives “to alter deceptively; especially : adulterate” as the first sense of the verb, in use since the fifteenth century.

A sophisticated act is, in the literal sense, a breach of integrity. Like someone serving colored water and calling it wine, or someone who fails the bar yet says they are a lawyer. Sophisticated attacker means a defender has been duped, in even the most basic way.

The self-flattering pivot of the word came very late. Etymonline dates “worldly-wise” to 1895, and the OED’s first citation for “complex or advanced” is C. S. Lewis in 1945, as Wordorigins reports. A breach statement that calls an attack sophisticated uses the youngest, and usually least applicable, sense of a word that meant a counterfeit for the prior five hundred years.

The modern sense therefore becomes a measure of the speaker, not the breach. In Was Stuxnet the “First”? I argued that calling an attack sophisticated mostly tells you the observer does not yet understand it. Verizon’s investigators had already said as much in their 2013 report, writing that attack difficulty “almost certainly reveals much more about the skill and readiness of the defender.” Lawyers then read the absence of the word as a confession of negligence, putting pressure on constant use as a get-out-of-jail card. Instead of claiming drunkenness and promising rehab, the executive claims the drink was complex and advanced. Thus the “sophisticated attack” became a confession of ignorance dressed up as a legal defense, one the courts have yet to accept.

2005 to 2010

An early clean admission came from Derek Smith of ChoicePoint, testifying to a House subcommittee on 15 March 2005. Criminals posing as small businesses had bought consumer files from his company. Smith apologized to consumers harmed by “criminals whose fraudulent activity ChoicePoint failed to prevent,” and when asked about warning signs he said “we should have recognized sooner the magnitude of that particular crime.” He described the criminals only by what they did.

The FTC fined ChoicePoint $10 million the following January because it “did not have reasonable procedures to screen prospective subscribers.”

Four months after Smith, John Perry of CardSystems Solutions showed the House how to talk out of two sides in one hearing. On 21 July 2005 he testified that “the attack on our system was very sophisticated.” Pressed later in the same session about the card data his company had kept, he said “we have stated that we were in error by keeping that data.” Visa’s witness at the same table said CardSystems had “knowingly and improperly retained magnetic stripe information.” I remember this case well, and CardSystems didn’t even use firewalls. Literally named “card systems” for payment cards, zero security.

The FTC’s complaint the next year described a SQL injection against a web application and found the company “did not implement simple, low-cost, and readily available defenses.” The words “readily available” run through the FTC’s orders of that period, against DSW, Guidance Software and TJX.

TJX took a third path. Its 2007 10-K described “the technology used by the Intruder” and an intruder who “had access to the decryption tool,” and left the adjective to the reader. My post on the TJX theft read that decryption tool as a key management failure. Canada’s privacy commissioners found TJX had protected its store wireless networks with WEP, which “can be defeated relatively easily.”

Ah, WEP. At a tech conference when WEP was first introduced I met with the 3Com engineers demonstrating the first WiFi routers with encryption. They had plastic cases with the SSID and password raised in the actual hard plastic.

What about rotation, I asked, since my secret should be a secret. They replied adoption needed ease of use, or there would be no encryption at all, secrets slow down use. Jesus WEP’d.

Hannaford Bros. disclosed in March 2008 and passed along a law enforcement assessment of a “new and sophisticated method.” In August 2009 the Justice Department indicted Albert Gonzalez for the Hannaford, Heartland and 7-Eleven intrusions, and its press release called SQL injection “a sophisticated hacking technique.” The adjective showed up as prosecution.

Robert Carr of Heartland Payment Systems then stood on a soap-box and said all of this out loud for the herd to hear. In August 2009 he told CSO that his assessors’ audits “were of no value whatsoever,” and in the same interview said “We need more humility” and “you can easily buy sniffer software off the shelf.”

This is my shocked face.

On 9 September he told SC Magazine “We thought we had protected ourselves, but we didn’t do enough,” and conceded “This was a website that they could get into.”

It was like “sophisticated” was finally going to be washed away.

Five days later he testified to the Senate about “the ever more sophisticated methods used by these cyber criminals.”

Damn it.

By July 2010 his first lesson for other executives was “Don’t blame other people.” Visa had answered the auditor complaint back in March 2009: “No compromised entity has yet been found to be in compliance with PCI DSS at the time of a breach.”

Word games. Compromise means non-compliant.

Verizon’s 2010 report, covering 2009 cases, found 96 percent of breaches “avoidable through simple or intermediate controls.” Sophisticated meant low bar, as in you aren’t doing the basics. Yet it clearly was being deployed for legal smoke to avoid charges of negligence.

2011

The argument for owning the basics really took off in 2011. Verizon’s April report repeated the news and said “90% of attacks are not highly sophisticated, and the method of intrusion is relatively straightforward in most cases.”

I spent that year giving talks on why Stuxnet was less sophisticated than its coverage claimed. By the time the antivirus vendors were hot-selling Flame in 2012, I could write “Apparently Stuxnet is no longer considered sophisticated.”

RSA’s disclosures that year carried both registers at once. On 18 March the illustrious Art Coviello described an “Advanced Persistent Threat” attack. Two weeks later RSA’s Uri Rivner explained that a phishing email had been “crafted well enough to trick one of the employees to retrieve it from their Junk mail folder,” and called the whole thing an “extremely sophisticated cyber attack.”

F-Secure later recovered the message. Its body read:

I forward this file to you for review. Please open and view it.

The attachment carried a Flash zero-day. The delivery was two sentences. Sophisticated.

Sony told Congress in May 2011 that the PlayStation Network intrusion was a “very carefully planned, very professional, highly sophisticated criminal cyber attack.” The UK Information Commissioner fined Sony in January 2013 and found “the attack could have been prevented if the software had been up-to-date.” Sony dropped its appeal that July with the line “We continue to disagree with the decision on the merits.” Citigroup said almost nothing about its own 2011 breach, in which account holders changed digits in the browser address bar and reached other people’s accounts. My old colleague Bruce Schneier called the missing control “kindergarten security.”

Honestly, I would expect better even from a kindergartener.

On 13 October 2011 the SEC’s Division of Corporation Finance issued its first guidance on cyber disclosure. It told issuers that detail amounting to a “roadmap” for attackers was “not required under the federal securities laws.” The Verizon statistic and the SEC guidance were just six months apart. From then on public companies drafted breach statements with permission to leave out the details, which is an invitation to turn adjective abuse up to 11.

2012 to 2016

Dropbox wrote a plain admission in July 2012, after passwords stolen from other websites were used against its users: “A stolen password was also used to access an employee Dropbox account.”

Target spoke out of both sides of its mouth. A spokeswoman said on 19 December 2013 “It is very clear it is a sophisticated crime.” Chief executive Gregg Steinhafel told CNBC “Clearly we are accountable and we are responsible.” Can it be both? The Senate Commerce Committee’s majority staff then documented stolen vendor credentials and security alerts that went unanswered, and quoted McAfee calling the point-of-sale malware “absolutely unsophisticated and uninteresting.”

A federal judge let the banks’ negligence claims proceed in December 2014 and wrote “Although the third-party hackers’ activities caused harm, Target played a key role in allowing the harm to occur.” The ruling was about what Target allowed to happen.

Dido Harding of TalkTalk delivered a plain answer in October 2015 on the BBC. Asked whether customer data had been encrypted, she said “The awful truth is, I don’t know.” Her company’s statements that month described criminals “becoming increasingly sophisticated.” Police arrested a 15-year-old.

I mean, it wasn’t a kindergartener, but still.

In December Harding told a Commons committee “Cyber security is a board level issue, and I am responsible for it.” The Information Commissioner’s penalty in October 2016 found “TalkTalk’s failure to implement the most basic cyber security measures allowed hackers to penetrate” its systems by SQL injection, through a database bug whose fix had been available “for over three and a half years.”

A very sophisticated amount of time.

In June 2015, four months before Harding’s BBC interview, the director of the US Office of Personnel Management told senators “I don’t believe anyone is personally responsible.”

2017 to 2022

Dara Khosrowshahi disclosed Uber’s concealed 2016 breach in November 2017 with a sentence that puts the whole failure on Uber: “None of this should have happened, and I will not make excuses for it.”

Richard Smith of Equifax wrote an ugly testimony the month before. The breach “occurred because of both human error and technology failures,” and the data was lost “at the hands of sophisticated cybercriminals.” The House Oversight majority found in December 2018 that “Such a breach was entirely preventable.” Capital One’s July 2019 filing blamed “a highly sophisticated individual” exploiting “a specific configuration vulnerability.” The OCC’s $80 million order the next year cited the bank’s “failure to establish effective risk assessment processes” before it moved significant operations to the public cloud. British Airways argued to the ICO that its attacker made conscious efforts to avoid detection. The penalty notice recorded that argument and then found a compromised supplier account without multi-factor authentication and administrator login details “stored in plain text.”

Perhaps most notably, the New York’s Department of Financial Services wrote lcamtuf’s sentence in October 2020 about the Twitter hijacking. Twitter had described “a phone spear phishing attack.” The regulator’s report called the attackers “a group of unsophisticated cyber crooks” using “basic techniques more akin to those of a traditional scam artist.”

Boom. There it is, although from a regulator.

Joseph Blount of Colonial Pipeline told the Senate in June 2021 that the ransomware crew entered through a legacy VPN profile that “did only have single-factor authentication.” In the same answer he said “It was a complicated password, so I want to be clear on that.” Blount defended his own concept of a “complex” password, and when Senator Portman asked whether multi-factor authentication should be used, he said “that is absolutely the correct advice.” He also said “We are accountable for our defenses.” Colonial then hired its first ever CISO, nearly a year after it had tripped over its clown shoes into a basic ransomware attack.

Optus produced a three-part record. Chief executive Kelly Bayer Rosmarin said of the September 2022 breach “it’s a sophisticated attack.” Home Affairs Minister Clare O’Neil said Optus had “effectively left the window open.” The communications regulator told the Federal Court in 2024 that the attack was “not highly sophisticated or one that required advanced skills” and was “carried out through a simple process of trial and error.”

The SMS phishing wave of summer 2022 shows an evolution. Twilio called its attackers “well-organized, sophisticated and methodical.” That’s like saying unknown kmown. Cloudflare titled its write-up “The mechanics of a sophisticated phishing scam and how we stopped it,” and the body reports that three employees entered their credentials and hardware security keys stopped the rest. In September Uber’s 8-K exhibit gave a literal account: “It is likely that the attacker purchased the contractor’s Uber corporate password on the dark web.” The contractor rejected repeated login approval requests. “Eventually, however, the contractor accepted one, and the attacker successfully logged in.”

2023 to 2026

CircleCI wrote a single sentence in January 2023: “While one employee’s laptop was exploited through this sophisticated attack, a security incident is a systems failure.”

Microsoft described its Midnight Blizzard intrusion in January 2024 as a password spray against “a legacy, non-production test tenant account” that “did not have multifactor authentication (MFA) enabled.” The Cyber Safety Review Board found the earlier Storm-0558 intrusion “was preventable and should never have occurred.”

Brad Smith answered in June that “Microsoft accepts responsibility for each and every one of the issues cited in the CSRB’s report.” The same testimony calls Russia’s SVR one of the “most sophisticated cyber agencies in the world.” By 2024 this annoying adjective had moved from the attack itself to the attacker’s employer.

Andrew Witty of UnitedHealth gave a one-sentence admission in written testimony on 1 May 2024: “The portal did not have multi-factor authentication.” He added “I am deeply sorry.” He delayed using the adjective for what happened until after entry, when the attackers “moved laterally within the systems in more sophisticated ways.” Senator Wyden called the missing control “cybersecurity 101.”

23andMe went the other direction and blamed its customers. Its January 2024 letter to plaintiffs said “users negligently recycled and failed to update their passwords.” It’s a good thing biometric login wasn’t blamed or the customers might have been accused of having poor DNA. The UK Information Commissioner fined the company £2.31 million in June 2025 and said “23andMe failed to take basic steps to protect this information.” At Marks and Spencer the chief executive and the chairman gave different accounts seven weeks apart. Chief executive Stuart Machin said in May 2025 “we were unlucky on this particular day through some human error.” Chairman Archie Norman told Parliament in July that social engineering is “a euphamism for impersonation” and that “it was a sophisticated impersonation.”

The SEC’s October 2024 order against Mimecast shows where the regulator takes its stand4. Mimecast’s January 2021 8-K said the company “has been compromised by a sophisticated threat actor” and said a “low single digit number” of customers had been targeted. The SEC found the actor had reached encrypted credentials for roughly 31,000 customers and fined Mimecast $990,000. The penalty attached to the understated scope. The adjective landed yet again.

Table time

Org Statement
2005 ChoicePoint “criminals whose fraudulent activity ChoicePoint failed to prevent”
2005 CardSystems “we have stated that we were in error by keeping that data”
2009 Heartland “We thought we had protected ourselves, but we didn’t do enough.”
2011 RSA “crafted well enough to trick one of the employees to retrieve it from their Junk mail folder”
2012 Dropbox “A stolen password was also used to access an employee Dropbox account.”
2014 Target “Clearly we are accountable and we are responsible”
2014 eBay “Cyberattackers compromised a small number of employee log-in credentials”
2014 Bitly “discovered an unauthorized access on an employee’s account”
2015 TalkTalk “The awful truth is, I don’t know.”
2017 Uber “None of this should have happened, and I will not make excuses for it.”
2017 Equifax “both human error and technology failures”
2018 Reddit “SMS-based authentication is not nearly as secure as we would hope”
2018 Marriott “We fell short of what our guests deserve and what we expect of ourselves.”
2019 Norsk Hydro “This Trojan software was discovered by our antivirus a few days later. But that was already too late.”
2019 Capital One “I am deeply sorry for what has happened”
2021 Colonial Pipeline “it did only have single-factor authentication”
2021 Kaseya “I feel like I let this community down”
2022 Okta “We want to acknowledge that we made a mistake.”
2022 Uber “Eventually, however, the contractor accepted one”
2022 Cloudflare “three Cloudflare employees fell for the phishing message and entered their credentials”
2022 Dropbox “We’re sorry we fell short”
2023 CircleCI “a security incident is a systems failure”
2023 Okta “an employee had signed-in to their personal Google profile on the Chrome browser of their Okta-managed laptop”
2024 Microsoft “did not have multifactor authentication (MFA) enabled”
2024 UnitedHealth “The portal did not have multi-factor authentication.”
2024 Ascension an employee download, likely an “honest mistake”
2025 Troy Hunt “I’m enormously frustrated with myself for having fallen for this”
2025 Coinbase “paying multiple contractors or employees working in support roles outside the United States”
2025 Marks and Spencer “some human error”
2025 Co-op “I’m devastated that information was taken”
2026 Carnival “gained access to an employee’s account via social engineering”
2026 Instructure “We focused on fact-finding and went quiet when you needed consistent updates.”

The answer

That leaves us back at lcamtuf’s sentence.

In July 2025 Clorox sued Cognizant, the contractor that ran its help desk, for $380 million over the 2023 breach. The complaint quotes the call in which a Cognizant agent answered an outside caller with:

Oh, ok. Ok. So let me provide the password to you ok?

Clorox’s lawyers wrote:

Cognizant “was not duped by any elaborate ploy or sophisticated hacking techniques.”

There it is. That is the sentence, filed in court by a breached company about its own attacker. Cognizant replied:

Clorox had “such an inept internal cybersecurity system.”

Children, settle down.

A breached company seems to have stepped up to call its adversary unsophisticated, the day that negligence sticks to someone else.

Why the CIA Chose Canada to Resettle Nazis After WWII

The newly released pages of Alti Rodal’s 1986 report have been read as a story of American deception and Canadian embarrassment. They support a narrower and more damning reading.

In 1953 and 1954 the United States had a path for legally admitting compromised intelligence assets. It chose, for a particular class of them, to move them into Canada under false identities instead. The records being released now explain what went into this decision. They also show Canada, once informed, objecting, tightening the channel, and then writing a screening doctrine that accommodated the practice that it had objected to.

The Maple reported the release of Chapter XII, Part 5 of Nazi War Criminals in Canada: The Historical and Policy Setting from the 1940s to the Present, which followed B’nai Brith Canada v Minister of Canadian Heritage, 2026 FC 1119. The newly visible material identifies George McManus, the CIA officer who asked Canadian screeners to accept American nominees without checks and who later served as the CIA’s representative in Ottawa; Oscar Holtz of the US Army’s Research and Resettlement Branch, which Rodal describes as a cover organisation for the CIA; and the figures of 39 men admitted and 52 rejected. Historian Jared McBride called it a ratline and asked where the American records are. Part of the answer has been in print since 1985, and the two sets of records read together describe a system rather than a scandal.

The legal option

Section 8 of the Central Intelligence Agency Act of 1949, referred to at the time as the 100 Persons Act, permitted the Director of Central Intelligence, the Attorney General and the Commissioner of Immigration, acting jointly, to admit up to one hundred aliens a year “without regard to their inadmissibility under the immigration or any other laws.” The provision existed precisely for people whose records barred them under ordinary law. It required a written determination by three named officials.

The General Accounting Office found it in use. In 1952 the CIA sought permanent residence for an asset convicted before the war of complicity in a political assassination. The request “included a justification which contained details about the subject’s background including his assassination conviction and the alleged terrorism acts,” and the three officials “agreed to admit the subject in the interest of national security without regard to his inadmissibility under any other laws.” GAO also described the CIA resettlement program established in the early 1950s for “some Soviet and East European defectors and some terminated CIA-employed aliens.” About thirty percent of its subjects were resettled in the United States, “and the majority of these were defectors.” The remainder went to other countries. For the American cases, GAO recorded that immigration law was observed and that State and Justice conducted a pre-immigration review.

The Canadian option

Rodal’s page 456 records what Holtz told Deputy Commissioner W.H. Kelly in 1954 when Canadian officials proposed that the Americans take their own nominees. The United States would decline because

the law of the country would not permit it, although there is now provision for them to take approximately 100 a year (The “100 Persons Act”), [one clause withheld under s. 13(1)(a)]

Holtz had already acknowledged that some of the men had “criminal records of which a number arose from cases involving moral turpitude — the category in which Nazi collaborators were included,” which was the statutory exclusion under the Immigration and Nationality Act of 1952. Kelly’s assessment was that “there is no desire to fill this quota if they can be disposed of elsewhere.” Rodal, on page 461, found that assessment plausible. Lester Pearson’s view at External Affairs was that the Americans “should take such people to the U.S., rather than unload them on others.”

The withheld clause is Holtz’s opinion of the Act. Justice Fothergill read it and described it as innocuous. Its absence changes little, because the structure is visible without it.

Route Record produced
Section 8 admission to the United States A written justification and a determination signed by three senior officials under the man’s name
Canadian Interdepartmental Committee on Defectors, December 1952 to April 1962 A case presented by the sponsoring agency to External Affairs for examination and approval
USAREUR nominee through the Karlsruhe visa office A biography prepared by the sponsoring agency and cleared by one sergeant, with that agency’s counterintelligence arm as the only reference

Each lawful channel attached an official’s name to an asset’s true record. The third channel attached nothing to anyone. The Americans used the first for assets they valued and the third for those they wished to be rid of, and Kelly identified the sorting rule at the time.

Why forgeries worked

Rodal’s finding on page 460 is that in the American zone “the only source of information consulted was the CIC, which was in fact working with USAREUR in the resettlement of former agents.” The RCMP regarded the Counter Intelligence Corps as “our best and only dependable source of information in the U.S. zone of Germany and Berlin,” and Kelly testified that no check on an Eastern European applicant was possible “apart from what was presented by the Americans, whether it was true or false.” An RCMP brief of April 1983, on page 447, set out the sequence: documentation arranged by the agency, a routine check referred to the same agency, a report of no adverse record, a visa. The screening system had a single upstream source, and the source had an interest.

The irregularities were detected outside that dependency. Visa officers in Stockholm reported falsified American documents to External Affairs in 1953, without consequence for a year. The Karlsruhe cases reached London after the death of the sergeant who had cleared them. The RCMP Commissioner wrote to Crean in September 1954 that men coming through the Research and Resettlement Branch “have obviously, in most instances, been supplied with false documentation,” that the RCMP was “not convinced that the figures which have been given to us in the first instance are in fact correct,” and that the same method had been used in other countries, “in some cases completely successful.” A request for the American files produced the reply that they had been destroyed, which Corporal Yetter of the RCMP, writing in 1983, considered unlikely for an agency that might want the men’s services again.

The method was already documented on the American side. The 1983 Department of Justice report on Klaus Barbie described the CIC’s employment of Barbie, its concealment of his whereabouts from France while extradition was sought, and his removal to Bolivia under a new name. Rodal opened her chapter with that case, and the 1983 RCMP report applied the same comparison to a Yugoslav CIC agent renamed in Austria in 1946 and landed in Canada in 1948.

The adjustment

The Canadian response, once the practice was understood, was procedural. Ottawa required that defector cases be presented by the CIA to External Affairs. It also recorded, on page 464, the principle on which such cases would thereafter be judged:

Obviously, the real purpose of resettlement arrangements would be defeated if the accepting country were to insist upon an unblemished past history. A person with such a history would not likely have been in the position to have rendered much service to the sponsoring agency.

For sponsored applicants whose agency was “not under the necessity of disposing of him quickly,” the Director for Security and Intelligence proposed that a clearance be issued so that the case would proceed “in the same manner as that of any ordinary applicant.” The Defectors Committee’s test for German ex-agents, set in April 1953, was that past Nazi connections “will not be of such a nature that disclosure here might prove embarrassing.” Washington made a parallel adjustment. GAO describes a mid-1950s CIA program under which the Agency itself conducted the background investigations “normally conducted by State Department visa personnel,” with the consent of State and INS. On both sides of the border the sponsoring agency became, by agreement, the vetting agency.

What the release shows

The Maple’s account treats the forgeries as the story. They are the symptom.

Two allied states maintained lawful procedures for admitting people their own laws excluded, procedures that produced signed records. A class of assets existed for whom neither state wished to produce such a record. Those assets traveled by the one route that left none, and when the route was discovered, the accepting state wrote a rule that spared future cases the inconvenience of a clean history. The single clause still withheld is one American officer’s remark about one American statute. Canada asked Washington in 2024 whether the remark could be released. Washington gave no answer, and the Canadian embassy treated that silence as a refusal.

The forest was published in 1985.

The Maple found a tree.

AI Warfare Targeting Black Authors: Wheatley to Kundizeza

The Academie Goncourt struck a novel from its longlist on 25 September, four days after an anonymous account with 92 followers declared it the work of a machine. The evidence was a single commercial detector. AFP ran the same passages through its own tool and got “very likely written by a human”, and seven other detectors disagreed with each other. The Goncourt cited plagiarism findings alongside the detector, but the plagiarism hunt began only because the anonymous account had made the author a target.

The author is Thelyson Orelien, 38, born in Gonaives, Haiti, resident in Montreal since 2010. His first novel, C’etait ca ou mourir, follows a teacher fleeing gang violence to Canada. It won the Prix du Roman Fnac on 21 September. The accusation from “Balance ton Claude” landed the same day. Within four days his Quebec publisher had suspended promotion, a book fair had withdrawn his guest of honour title, two newspapers had found copied passages in a short story and columns he wrote between 2012 and 2014, and the Goncourt had acted “to preserve the integrity of the Goncourt Prize” and its mission of honouring “literature written by women and men.”

On 24 September Le Figaro identified the account’s operator as one of its own columnists, Samuel Fitoussi, author of Woke Fiction. He had denied involvement to AFP all week while reposting the accusation from his named account. On 25 September he confirmed a “collective project” whose other members remain unnamed, and called the question of race conspiracist. The president of the Academie Goncourt, Philippe Claudel, had already told franceinfo why he thought the timing mattered: a Haitian, Canadian, Black, francophone foreigner, in a season when passions run high.

Fitoussi’s stated motive is fear that AI will end human writing. He is an associate member of Frst, a Paris fund that finances AI startups and began life as Otium Ventures under the Catholic billionaire Pierre-Edouard Sterin. The detector he relied on, Pangram, raised $9 million in July in a round led by Menlo Ventures. Menlo’s partner wrote that the firm led the round as part of the Anthology Fund, the vehicle it runs with Anthropic, whose assistant gave the account its name. Pangram describes its detector as a model trained on tens of millions of documents known to be written by humans.

The Goncourt was the second prize of the year to act on that detector. On 14 May the Commonwealth Foundation named five regional winners of its short story prize. A Wharton professor ran the Caribbean winner through Pangram, “The Serpent in the Grove” by Jamir Nazir of Trinidad, and posted the result: 100 percent AI. Granta, which published the winners, asked Claude whether the story was machine written and put the answer in a statement. Its publisher Sigrid Rausing wrote that the judges may have awarded a prize to AI plagiarism and that Granta might never know. On 19 June Granta ended its external publishing partnerships. On 22 June the Foundation cleared all five winners. It had refused to run detectors on unpublished work and instead asked every winner for working drafts, time-stamped documents and notes. Nazir was named overall winner on 30 June. Vauhini Vara of The Atlantic then fed fifteen years of winning stories into Pangram and found that the only ones it flagged were three of the five from 2026.

On 6 October the Caine Prize for African Writing gave its £10,000 award to “The Blue Fighter” by Simbarashe Steyn Kundizeza of Harare, chosen from 407 entries across 27 countries. On 11 October Vara published her Pangram scan of the story under the headline “Yet Another Literary Prizewinner Seems to Be AI”. The detector flagged almost the whole text. It had passed every earlier Caine winner she tested and “The Whistleblower”, a thriller Kundizeza published in 2021. His agency told her it has full confidence the work is his. The same day the Caine Prize Foundation opened a review. Vara noted in the article that detectors flag the tidy English of writers for whom it is a second language. Stanford measured this in 2023: seven detectors were near perfect on essays by American eighth graders and flagged 61 percent of essays by non-native speakers as machine written.

The accused writers in May, September and October came from Trinidad, Haiti and Zimbabwe. The detector was the same each time.

Zimbabwe has seen this office before. In 1954 the Southern Rhodesia government set up the African Literature Bureau. Its stated purpose was to grow a reading market in Shona and Ndebele. Its working purpose was to screen every manuscript by an African before a publisher could print it, and to keep politics out. Solomon Mutswairo’s Feso, among the first novels by an African, came out under the Bureau in 1956, and the Ministry of Education later struck it from the reading list for African schools. Philemon Mutambara, a teacher with a Fort Hare degree, submitted a Shona novel in the 1960s. The Bureau returned it with demands for changes and a reader’s report telling him that the books it had already published “would be an invaluable guide to you as the sort of standard required for publication.” He refused, died in 1968, and the novel appeared 51 years after he wrote it. A white office in Salisbury held a model of what an African story should read like and graded manuscripts against it. Flora Veit-Wild, who wrote the social history of that system in Teachers, Preachers, Non-Believers (1992), later interviewed the Bureau’s post-independence director, who told her there had been no censorship, only screening. Pangram holds a model of what a human story should read like and grades manuscripts against it. It flagged a Harare writer’s prize story and passed the one he wrote in 2021.

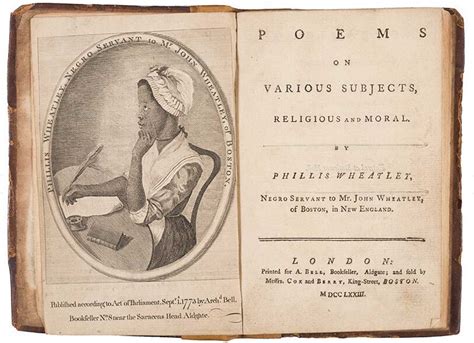
Black authors in the French and English worlds have been asked to prove they wrote their own books for 250 years. Phillis Wheatley was examined by eighteen Boston men in 1772, Governor Thomas Hutchinson among them, before a London publisher would print her poems, and their signed certificate opens the 1773 edition.

Bakary Diallo, a Senegalese rifleman, published Force-Bonte in Paris in 1926 and was assumed for decades to have had it written by his French patrons. Camara Laye’s Le Regard du roi (1954) was attributed in 2002 by the scholar Adele King to two Belgians in Paris, his landlord and a reader at his publisher. Yambo Ouologuem won the Renaudot in 1968 for Le Devoir de violence, faced plagiarism charges from 1971, and published nothing after 1972.

A white author gets the opposite treatment. Michel Houellebecq copied Wikipedia passages into La Carte et le Territoire, admitted it, called it collage, and won the 2010 Goncourt anyway.

Nazir handed over his drafts and timestamps to keep his prize. Orelien is compiling a dossier with his editor to prove he wrote his own book. Kundizeza’s agency is vouching for him while a foundation reviews his story. Wheatley stood before eighteen examiners in Boston over 250 years ago.

The information warfare against Black authors hasn’t changed much.