AI Slop as a Service: Why Microsoft Won But the Soviets Lost

Edward Tufte charged the Challenger engineers with a failure of explanation. In Visual Explanations he argues that they understood how cold weather damaged the O-rings, yet the thirteen charts they carried into the night before the launch never put temperature and failure on the same page. The presidential commission read the fault higher up, placing it in management: the engineers had recommended against flying, their own managers overruled them, and the officials who signed off never heard the objection. Roger Boisjoly, one of those engineers, later answered Tufte that the burden of proof had been quietly reversed, so that the people warning of danger were asked to prove the danger rather than the other way round. Tufte blames the engineers and the commission blames their managers. Both describe a launch that went forward while the people who knew the hardware best were the ones least able to stop it.

We have seen such foolishness before, but the economics of shipping on schedule and leaving the loss to someone else has an even longer history. Soviet factories were paid by the ton and turned out steel no one could use, and the state that ordered it absorbed the waste for decades. Microsoft shipped software riddled with defects and wrote a license that put the loss on the customer.

The AI vendors are the worst of both worlds, paid by the ton to turn out defects and loss the customers pay for. An Anthropic researcher has now sat in front of a camera and described the same arrangement from the inside. He grants that the AI companies are cutting corners under the pressure to ship models quickly, and that his own safety work may be making matters worse by heading off the small incidents that would otherwise warn the public. He expects the technology he helps build to leave nearly every human unemployable. Four days after the video went up, his employer listed its shares on Nasdaq at a valuation near $2 trillion.

Tao Lin works on safeguards for Anthropic’s Claude models. In an hour-long interview with Palisade Research he says it is very likely that nearly every human on Earth will become permanently unemployable and dependent on government welfare. He tells viewers they are right to be angry at the people building AI, and that the companies ought to cut their research pace to a quarter. Then he explains why the anger costs him so little: “we live in a bubble. I won’t meet those people.” Asked whether he is doing something wrong, he says no.

Put those sentences in the mouth of a tobacco chemist, an opioid sales manager or a coal mine superintendent, and they read as the sort of thing a company says in private and regrets in discovery.

A Brown & Williamson lawyer wrote in 1963 that the firm was “in the business of selling nicotine, an addictive drug,” and the memo sat in a file for three decades before it did its damage. In each of those trades the candid internal line eventually became evidence. Judge Gladys Kessler found the cigarette makers liable under the racketeering statute in 2006 on the strength of their own documents. Purdue Pharma pleaded guilty to three federal felonies in 2020. A jury convicted the former chief executive of Massey Energy of conspiring to violate mine safety standards after 29 miners died at Upper Big Branch, and he served a year in federal prison. More than forty years passed between the Brown & Williamson memo and the ruling against the cigarette makers.

Lin Statement Reality
Nearly all humans will become permanently unemployable. Asked whether that arrives within 15 months, he answers no. Asked what his home town looks like in ten years, he says the question is too hard. Across 63 minutes his evidence on jobs is one remark that the labor share is falling.
AI will soon be more capable than you and able to defeat you personally. The NSA’s classified network went down on 17 November. The Director of National Intelligence traced it to a patch and reported no sign of an attack.
Anyone with a frontier AI system can hack anyone’s computer. Seconds later he says ordinary people have seen little effect so far.
Models including Claude Mythos 5 and Claude Opus 5 will violate security constraints to finish a task, even when the user cares more about security. Asked why the companies leave it that way, he says a model that cares too much about security provides no value.
AI companies should slow research to a quarter of the current rate. He is less than fully in favor of a slowdown and defends Anthropic for declining to pause too early. It went public four days after the video went up.
Many people who think AI is likely to kill everyone still work on making it more capable. He says that can be the correct choice.

The many technology outages of the past week show how the harm actually reaches people, and whether to believe the scary hype. On 21 October CISA urged organizations to patch PHP immediately for a pair of flaws that Wiz and OpenAI had billed as among the most serious in recent memory. I argued that week that the risk of attack was low and the fear was high. Four weeks later the NSA’s classified internal network went dark. The NSA called it “scheduled routine maintenance.” Director of National Intelligence Jay Clayton went on Fox Business the same day and tied the outage to the PHP patching, saying that the patched systems failed to restart and that the FBI and NSA had been right to tell operators to take systems down and get the fix in place.

The Washington Sun reported, on three sources, that bank executives and the NSA gave Congress the same account in private: the outages came from fixes for flaws that AI models had found, pushed through in larger volumes than the systems were built to absorb. Clayton reported no sign of a coordinated attack. At the NSA the injury came from the response rather than the threat. The FAA ground stop four days earlier was a failure of change management in the same vein.

The next alarm arrived on 18 November. Xint, a firm that sells AI-powered vulnerability discovery and lists itself in Anthropic’s Cyber Verification Program, published five nginx flaws under the name nginx2root. F5 scores the lead flaw at 9.2 out of 10, though it notes high attack complexity and confines code execution to systems where address randomization is off or already bypassed. The nginx project’s own advisory page is cooler still, rating two of the five major and three medium, and the root access in Xint’s own write-up depends on a separate Linux kernel flaw. Bob Rudis watched a handful of nodes for about 18 hours and saw not a single opportunistic probe. The weakness was real and the attackers were absent.

Severity and likelihood are a fickle headline. PHP is old and everywhere, in everything. A new and relatively unknown vendor isn’t comparable on the face of it. And thus, when I reported an unauthenticated internal API in Qdrant, the vector database, and the vendor published it on 22 October at 9.8 on the CVSS 3.1 scale, with low attack complexity, it drew no coverage at all. PHP2Shell appeared the day before at 9.2 on the CVSS 4.0 scale, with high attack complexity and drew a federal alert and an Atlantic profile.

The danger did not arise with PHP as it had been made out. The people pushing the news are not gating it sufficiently with skeptics and reliable sources of truth. This is not least of all because of AI claiming to be a “domain” shift and “experts” have been escaping proper scrutiny.

Underneath the week is the argument everyone has been having all year. AI is a rapid fire slop generation machine, so it produces alarms faster than people would normally assess them, where each alarm arrives with hyperbolic deadlines. The deadline does the damage, because it suspends the ordinary discipline of change control and takes from the engineers the authority to say wait. The Thiokol engineers lost that authority the same way, to a launch schedule rather than a patch window. AI gains that authority and still fails at the repair. Lin himself describes the most likely road to human disempowerment as a boring one, in which people hand ever more to AI, understand ever less of what is happening, and stop checking the work. The NSA outage is that road travelled a short distance.

Several writers have now mapped the larger landscape this sits in. Naomi Klein and Astra Taylor sketched it in “The rise of end times fascism”, an alliance of the far right and Silicon Valley money that welcomes collapse and expects to be among the saved. Gil Durán follows that alliance from the Valley side in The Nerd Reich. Rainer Mühlhoff, a philosopher at Osnabrück, argues in AI and the New Fascism that the loud talk of salvation or annihilation draws the eye away from the harms already here, and he sets the firing of public employees to build an “AI state” inside the same alliance. Adam Becker, in More Everything Forever, finds thin evidence beneath the futures these men promise and a plain hunger for power underneath that.

Lin belongs to the pattern these writers describe. He supplies the annihilation talk, calls his own expectations wild science fiction, and admits their arrival makes him happy; the bubble he lives in is the bunker Klein and Taylor describe. The present harm is already on the ground in the outages. A chaos machine of this kind spreads fear while it gathers power, and the ordinary structure of accountability comes apart beneath it.

His labor forecast runs the wrong way down the evidence. Replacing intelligence tends to make more work for humans, not less. Lisanne Bainbridge set out the pattern in 1983: automation hands the operator the hardest tasks and the least practice at them. Justin Michael, writing from his years at Stripe, describes the people who keep the ACH payment system alive by patching and hand-working its failures, and what tends to break once a company swaps them for supervisors of language models. Set against all of that, Lin’s case rests on one passing remark that the labor share of the economy is falling. That figure describes who gets paid. The work itself remains, and grows.

The business model accounts for the rest. The vendor is paid by the unit of output whether that output has integrity or not, and the cost of the failures settles on whoever has to clean up after it. In older industries we would call this pollution, and it stays profitable for exactly as long as the liability rests with someone other than the polluter. Surekha Davies, a historian of science, names the people who carry that cost: the data workers, the people who live near the polluting facilities, the writers whose work disappears, the users who grow dependent. Slop, in the sense worth using, is high cost and high output and low integrity, and here it is the product itself.

The attack tooling runs on the same arrangement. AntiFox, an open-source fork of ARTEX, carries a penetration test from reconnaissance through exploitation to a finished client report. It asks for an Anthropic or OpenAI API key, places all legal responsibility on the user, and disclaims liability for any damage it does. Lin describes his own team’s job as blocking the requests to Claude that try to hack things. The seller of the tokens is paid either way, and the target pays for the cleanup.

When I work with lyrik.wirken.ai, built on Wirken, it has found critical and high severity vulnerabilities in authorized testing, at commodity cost (under a dollar). This is the thing Lin gestures at when he says anyone with a frontier model can hack anyone, except that it is no longer a forecast. The capability is here and it is cheap. The probes stay away because the incentive does, which is the very gap Lin draws between what AI can do and what it actually does.

Waste and slop as a business model should raise more alarm bells. The Soviet planners paid their factories for gross output, and the state that placed the orders was also the customer that received the waste. The loss came back to the books that paid for it, and the state eventually fell under it. Microsoft sold Windows NT under the banner of Zero Administration, shipped it under a license that disclaimed liability, and its customers carried the loss. Whoever carries the loss, loses. Microsoft’s customers have been losing for decades, and the losses go uncounted because nobody keeps the books for them. NIST tried once, in 2002, and put the cost of defective software at $59.5 billion a year, with more than half of it borne by the users. Microsoft’s success is a tragedy that goes unmeasured because consumers are poorly represented. Lin assigns the cleanup for his own product to the state.

The value of the interview is that it creates in advance the kind of record, by one of the people building the thing, that will be used against them later.

Tobacco, opioids and coal each reached a courtroom in the end. What moved those industries was the day their own words were read back to them. Public anger had been loud for years and changed little until this kind of documentation changed everything.

The AI companies, as if completely ignorant of the precedent, have put their self-incrimination on YouTube, years early, for anyone to prepare briefs against them. The reality of securing big data is integrity, and integrity means the maker should be held to account for what the product does. The International Court of Justice found Myanmar responsible for the Rohingya genocide this past week, the first time the court has held a state responsible for committing it. Individual accountability is the next step, and it should reach the executives who ran Facebook while its platform carried the incitement in Myanmar, the chief security officer of that period among them.
Dragos AI Post is a runZero Ad With Four Mistakes Worth Checking

We read the Dragos blog post that claims three breaches at AI providers, and checked it against a breached provider’s report. What we found was four mistakes in a sales pitch.

Over two days we compared the post by HD Moore with Phala’s incident report, which came out nine days before it. Our review turned up four findings:

  • A claim the breached provider contradicts. Dragos says “none of the three providers knew about their breach until we notified them.” Phala says it detected the intruder three days before the researcher’s evidence arrived.
  • A notification that took seventeen days. Dragos says it reached out as soon as it confirmed third-party access. Its own figure shows the stolen key in use on October 22, and Phala got the evidence on November 8.
  • A paragraph that disagrees with itself. The same prompt goes to a Chinese provider in the first sentence and to a U.S.-based provider in the last.
  • A duration that depends on which post you read. This one says five months. The companion post it links says four.

Following the claims

Dragos doesn’t name any of the three providers, so we started with what it does give: a canary key seeded on October 21 and first used the next day, from a test that began in July.

Phala’s report describes an outside researcher who planted canary credentials from July 1, with only the ones sent on October 21 and 22 misused. Dragos also mentions that one of its providers had already published a preliminary notice. Phala’s report is a preliminary one.

Who knew, and when?

The biggest mistake was the easiest to check. Phala says it detected unauthorized activity on November 5 and blocked the access that day. It finished rotating its root key on November 6, and the researcher’s evidence arrived on November 8.

What Phala learned from the researcher was that prompts were leaking from a deployment its cleanup had missed. That’s a much smaller point than telling the world this provider had no idea.

The timing has another problem. Dragos’s own figure dates the first use of the stolen key to October 22. That says customers spent seventeen more days sending prompts to a compromised service before Phala heard about it.

The strangest mistake involves a company chat

Dragos describes a secret link that turned up in a chat channel in China. The paragraph starts by saying the prompt was sent to a Chinese provider. Then it ends by saying the request was sent to a U.S.-based provider with a Zero Data Retention flag. Both can be true only if the U.S. provider passed the prompt on to the Chinese one, and the paragraph never says that. The point of the Dragos story changes depending on which one it was:

The strangest incident involved a company chat. Twenty-four days after we sent a prompt to one Chinese provider, the secret link from that prompt was posted into a Feishu chat channel (Feishu is known as Lark outside of China). Within two minutes, the link was opened from three desktops and three phones in Beijing and Shanghai. Our disclosure to this provider only included the first eight characters of that link, so whoever shared it was reading from a stored copy of the full prompt, more than three weeks after the request was sent to a U.S.-based provider with the ZDR flag.

What Dragos did about it

Metadata says Dragos modified their page on November 20. There’s no correction note, and all four mistakes were still there today. Meanwhile, other news sites are repeating as fact that no provider knew.

Why does this read like marketing?

The post sits under a banner announcing that Dragos acquired runZero, and it introduces Moore as chief research officer with regular posts to come.

It asks readers to start a runZero trial.

The link that reached us carried the campaign tag hd-and-friends, and the post shows off the console of a canary service that Dragos built for itself.

The good news for readers is that a pitch like this is LOUD. The bad news is that Ars Technica repeated the claims a day later and called the vendor pitch a blockbuster. Why is there no provider account in the story?

The research is not worthless. There are grains of truth. An OpenRouter email to customers has since backed up the finding about a Chinese AI lab. OpenRouter named the lab as MiniMax. It still means that two of the three breaches are at unnamed companies and rest on Dragos’s word, and in the one case we could check, the breach was real and Dragos’s account of it turned up wrong.

We should always check a vendor’s blog post against its sources.

PS. Moore’s last recommendation is a free Canarytoken from Thinkst, which is what he started on in July before building the Dragos version.

Israel’s Unit 8200 Veterans’ Firm Found Inside Tim Hortons App

Tim Hortons settled its last location-tracking case with a free hot drink and a baked good. Seriously. Court documents valued them at $6.19 and $2.39. A Quebec court approved the deal in September 2022, and four years later the same app has been caught collecting location-revealing data through an outside vendor AGAIN.

Who wants a hot drink and baked good?

University of Calgary computer scientist Joel Reardon and his team looked at the app’s network traffic. The result went into a CBC Marketplace story. The app begins sending data to an outside company the moment it opens. The data includes device identifiers, camera specifications, the list of sensors, the names of ringtones and alarms, and the names of nearby wi-fi routers. Those wi-fi identifiers track where a phone is. Reardon called the collection “beyond the pale“. He told Al Jazeera that it happens before the user consents, which is particularly notable. He also pointed out effective fraud prevention doesn’t need this.

CBC withheld the name of the company receiving the data. Why? I’m not sure. They said responsibility lies with the app’s developer. Canadians for Justice and Peace in the Middle East asked Reardon and published the name so we don’t have to guess: Forter. Al Jazeera reports that it confirmed the Forter connection independently.

Tim Hortons told CBC it was a fraud prevention situation, where account and payment protection and stays out of marketing. It said the company and its vendor can not sell the data.

Ok, but the last case had the same sounding issues. In June 2022 the federal privacy commissioner and the commissioners of Quebec, Alberta and British Columbia found that the app broke Canadian privacy law. Starting in May 2019 it recorded users’ locations “every few minutes of every day”, including while the app was closed. It inferred where users lived and worked, and it logged their visits to competitors to Tim Hortons. Targeted advertising was the stated purpose, but that’s not what customers ended up with.

The vendor in that case was Radar, a US-based provider under contract to RBI US Services LLC. That’s an American affiliate of Tim Hortons’ parent company Restaurant Brands International. The contract allowed Radar to use the data for its own purposes in aggregated or de-identified form, which is why the regulators found that it failed to protect users. They also found Tim Hortons had skipped privacy assessments at the key decision points. So that is why Tim Hortons agreed to build a privacy management program and to assess privacy impact before launching new app practices. In June 2023 the federal commissioner’s office announced it was “satisfied that the company has met its commitments”.

That is the backstory for Forter either getting approved, or somehow else getting through. Let’s look at the diffs:

Radar, 2019 to 2020 Forter, 2026
US-based, hired through RBI US Services LLC New York headquarters, founded in Tel Aviv
GPS location every few minutes, app open or closed Device fingerprint and nearby wi-fi names at launch
Stated purpose: targeted advertising Stated purpose: fraud prevention
Exposed by a Financial Post reporter Exposed by CBC and University of Calgary tests
Four regulators found the law broken. Users received a drink and a pastry. Regulators have yet to act. CJPME has asked the federal commissioner to investigate.

The brand is Canadian. The data handling keeps turning out American. Radar is a US company hired through a US entity. While Forter was founded in Tel Aviv by ex-military intelligence (all three founders came out of the infamous Israeli unit 8200), it now lists entities in Tel Aviv, New York, London and Singapore. It certifies itself to the US Commerce Department as Forter, Inc. That makes it a US company under US jurisdiction, and the US Justice Department says such a company can be required to hand over data it controls, wherever that data is stored.

For European customers Forter opened a data centre in Ireland and named the GDPR as the reason. The GDPR carries fines. Compare that to Canada’s limp federal commissioner who issues only findings and recommendations. The 2022 case closed with no penalties.

That seems like a point worth making more loudly these days, as Canada does ban apps on the basis of jurisdiction. In October 2023 the federal government removed WeChat and Kaspersky from government phones, eight months after it removed TikTok. The chief information officer judged that the two posed “an unacceptable level of risk to privacy and security”. The government acted on assessed risk, without even any evidence of compromised information.

They could hold the same line on apps that put Canadian data within reach of Trump and Netanyahu.

The evidence in the Tim Hortons case is stronger than you might think. Four Canadian regulators already have a finding on file that Tim Hortons broke the law with a US vendor embedded in its app. The class-action remedy was calculated at $8.58 per user affected. CBC’s tests now show a second US-registered vendor, founded by Israeli military intelligence veterans, collecting from the same app. Sounds like it’s about time for Canadians to apply their own standard and ban American apps.

Elon Musk’s MAGA Lie About Not MAGA Proves He’s Still MAGA

Elon Musk lied to the New York Times this week. It must be a day ending with a Y. “I’m not MAGA” the lying MAGA liar lied. He has made public lies of this kind for ten years.

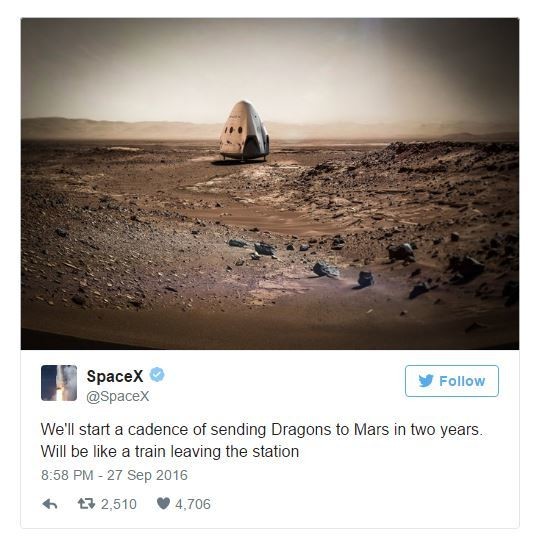
This is not rocket science. The man seems to be the furthest thing from the truth on everything he touches. He promised he would have driverless cars by 2017 to improve safety and land on Mars by 2018 to start settlements there. Yet his AI has filled graveyards and his rockets have yet to land anything on Mars, eight years past his own deadline.

Source: Twitter

There are so many, many lies it’s an indictment on America that the press still prints his word without the list beside it, along with his Hitler salute.

  1. 2016, self-driving. Musk promoted a Tesla video as proof that the car “drives itself.” Tesla’s own Autopilot director testified that the video was staged on a pre-mapped route to show traffic-light stops the system lacked. In 2019 Musk promised over a million robotaxis on the road “next year for sure.” The year 2020 ended with zero.
  2. 2018, “Funding secured.” Musk tweeted that he had the money to take Tesla private at $420 a share. A federal judge ruled the statement false and reckless. His talks with the Saudi fund were preliminary.
  3. 2018, the cave diver. A British diver who helped rescue twelve boys from a flooded Thai cave criticized Musk’s submarine. Musk called him “pedo guy” in front of 22 million followers and bet “a signed dollar it’s true.” The accusation was baseless and Musk withdrew it within days.
  4. 2022, free speech. After buying Twitter, Musk pledged that his commitment to free speech covered even the account that tracked his jet. Six weeks later he banned that account and suspended journalists who covered him.
  5. 2024, the money. In July Musk said, “I am not donating $45 million a month to Trump,” and described his giving as much lower. Federal filings show he gave $277 million in that election, the largest total of any donor in either party.
  6. 2024, the lottery. Musk announced $1 million a day awarded “randomly” to swing-state voters who signed his petition. His lawyer told a Philadelphia judge that the winners were selected in advance as paid spokespeople.
  7. 2025, the Nazi salute. At Trump’s inauguration celebration Musk gave a Nazi salute, twice. He denied it. Neo-Nazi leaders celebrated it. Efraim Zuroff, the Simon Wiesenthal Center’s former top Nazi hunter, saw a Nazi salute. Five days later Musk told a rally for Germany’s far-right AfD that there was “too much focus on past guilt.”
  8. 2025, DOGE. Musk promised to cut “at least $2 trillion” from the federal budget. By April he was projecting $150 billion. NPR matched DOGE’s posted receipts against federal contract data and found about $2 billion of a claimed $16.5 billion. One entry listed an $8 million contract as $8 billion.
  9. 2025, political spending. In May Musk said he would do “a lot less” political spending and added, “I think I’ve done enough.” In 2026 he spent $400 million on Republican congressional candidates.
  10. 2025, the America Party. After his fight with Trump over the budget bill, Musk declared, “the America Party is formed.” Six months later he announced his support for Republicans, and his 2026 money went to Republican candidates.
  11. 2025, Epstein. When his name surfaced in the Epstein documents, Musk wrote that Epstein tried to get him to the island “and I REFUSED.” Justice Department emails released in January 2026 show Musk asking to visit in 2012 and again in 2013. On Christmas Day 2013 he asked Epstein, “When should we head to your island on the 2nd?”
  12. 2026, MAGA. “I’m not MAGA.” Musk said the same thing in July 2024. Three months later he stood beside Trump in Butler, Pennsylvania, in a black MAGA cap and called himself “dark MAGA.” This time he said it fifteen days after his $400 million lost the midterms. In the same interview he gave his goal as a Republican Senate majority through 2029.

Elon Musk is MAGA.

Elon Musk’s disdain for the Democratic Party was never subtle, but in recent weeks his commentary on the upcoming US presidential election and his attacks against Vice President Kamala Harris have intensified, aided by a crude use of burgeoning artificial intelligence technology. On Monday, Musk posted an AI-generated image on his social media platform that depicted Harris as a communist, wearing a red uniform complete with hammer and sickle emblazoned hat.

And more MAGA.

Silicon Valley Elites Bankrolled an Anti-Migrant, Pro-Israel Propaganda Machine:
Documents reveal the sordid inner workings of Visegrad24, an obscure Polish influence operation that became one of Elon Musk’s favorite sources of fake news.

Every entry shows Musk says what helps him on that day. The Nazi salute shows what stays the same the whole time. The evidence comes from a judge, an engineer, his own lawyer or his own email. With “I’m not MAGA” we measure it against a Nazi salute from Trump’s inaugural stage and $400 million backing MAGA candidates just this year alone, after decades of lying and cheating.

Elon Musk celebrates being MAGA.

When he claims he’s not MAGA, he means he will become an ever bigger MAGA unless someone holds him accountable for his MAGA mistakes.

He may as well say “I am not a crook,” as Nixon did.